Skip to content

Menu

LexBlog, Inc. logo
NetworkSub-MenuBrowse by SubjectBrowse by PublisherJoin the NetworkGet StartedSubscribeSupportContact
Search
Close

The EU KIDS Act Proposal: Towards a New Regulatory Framework for the Protection of Children Online

By Dan Cooper, Dita Charanzová, Jadzia Pierce, Anna Sophia Oberschelp de Meneses, Shona O'Donovan, Sam Jungyun Choi, Virginie de France & Edwin Djabatey on September 21, 2026
Email this postTweet this postLike this postShare this post on LinkedIn

Table of Contents

  • Scope
  • The Framework
  • 1. Delaying children's access to certain social networking and video-sharing platform services
  • How Would Age and Parental Responsibility Be Verified?
  • 2. Embedding Child Safety into Product Design  
  • What about Operating Systems?
  • What Other Rights, Governance and Compliance Obligations Would the KIDS Act Proposal Introduce?
  • Enforcement
  • Looking ahead

On September 17, 2026, the European Commission (the “Commission”) published its proposal for a new EU framework on child safety online (the “KIDS Act”). The proposed Regulation aims to introduce EU-harmonized age-based account restrictions, safety-by-design rules, and age-assurance obligations across a broad range of digital services and systems.

The proposal is the latest of a growing body of initiatives aimed at strengthening children’s safety and privacy in the digital world, both in the EU and globally, as discussed in our recent blog post.

This post summarizes some of the KIDS Act’s key features.

Link to Scope Scope

The KIDS Act, as proposed, would have broad extraterritorial reach and apply to the following services (collectively, “Covered Services”):

  • online social networking services;
  • video-sharing platform services;
  • software application stores (i.e., app stores);
  • online games;
  • operating systems;
  • AI companions (i.e., AI systems, including general-purpose AI systems, that provide sustained, personalized interaction or companionship and simulate or facilitate social, emotional or interpersonal relationships with users); and
  • general conversational chatbots.

The proposal also establishes some exclusions for services and systems that, in the Commission’s view, are unlikely to pose significant risks to children (i.e., any natural person under the age of 18). These include certain open-source software development and sharing platforms, and services and systems specifically developed and operated exclusively for scientific research and development.

Link to The Framework The Framework

The proposal “specifies and complements” the EU Digital Services Act (“DSA”) (particularly Article 28) and “complements” the EU AI Act. The KIDS Act would establish two main sets of obligations for in-scope digital service providers operating in the EU: (1) delaying children’s access to certain social networking and video-sharing platform services; and (2) embedding child safety into the design and operation of in-scope digital services.

Link to 1. Delaying children’s access to certain social networking and video-sharing platform services 1. Delaying children’s access to certain social networking and video-sharing platform services

The KIDS Act would generally prohibit users under the age of 15 from creating accounts with and having access to certain social networking and video-sharing platform services, with limited exceptions. The applicable exceptions would depend on the child’s age and, in some cases, require a parent or guardian to authorize and manage their child’s access to the service. Where a parent or guardian creates or manages an account for a child, the provider would be required to take measures to verify that the adult holds parental responsibility for that child.
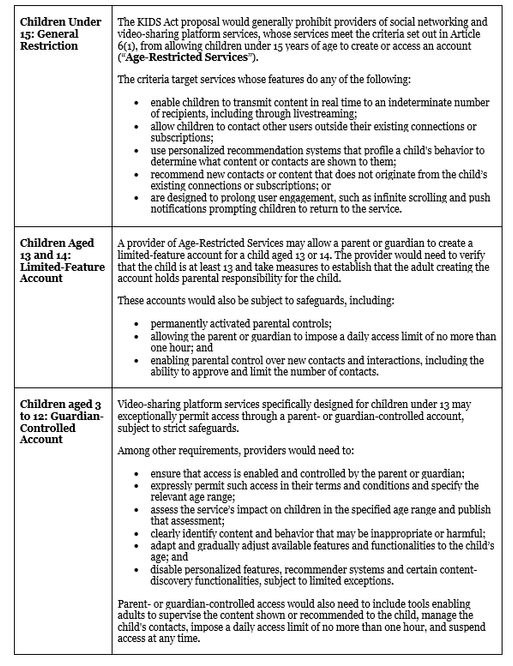
Link to How Would Age and Parental Responsibility Be Verified? How Would Age and Parental Responsibility Be Verified?

Providers of Age-Restricted Services would be required to rely exclusively on third-party EU age verification solutions using EU proof-of-age attestations certified under the “EU Age Verification Scheme” for purposes of complying with the under-15 ban and its derogation for 13-14 year olds. The Commission would maintain and publish EU-wide lists of certified age verification solutions and providers of proof-of-age attestations. The proposal further provides that European Digital Identity Wallets certified under the eIDAS framework and compliant with the EU Age Verification Scheme are deemed certified for these purposes. For purposes of compliance with the more broadly applicable safety-by-design obligations and app store requirements, providers are permitted to use alternative age-assurance solutions so long as they meet certain standards (to be further specified by delegated acts).

Notably, within six months of the KIDS Act taking effect, providers of Age-Restricted Services would be required to establish whether holders of existing accounts are under the age of 15. These providers would need to disable accounts where the user is determined to be under 15, as well as accounts where the user’s age cannot be established. Those providers designated as Very Large Online Platforms (“VLOPs”) under the DSA would also be required to submit a detailed compliance plan that, per Recital 62 of the KIDS Act, must corroborate, from a technical and robust evidentiary perspective, the “high degree of confidence” standard for determining whether the recipient has reached the age of 15.

The KIDS Act proposal also establishes a framework for verifying parental responsibility where a user seeks to create or manage an account on behalf of a child. Providers may rely on public registries, existing parental relationship signals, or (for a time) self-declarations subject to reasonable verification measures, provided that the process remains privacy-preserving and does not enable the provider to track, profile, or geolocate the adult or child concerned.

Link to 2. Embedding Child Safety into Product Design   2. Embedding Child Safety into Product Design  

All providers of Covered Services (except operating systems) would generally be required to implement a range of measures aimed at ensuring a high level of privacy, safety and security for children. The applicable requirements would vary depending on the type of service.
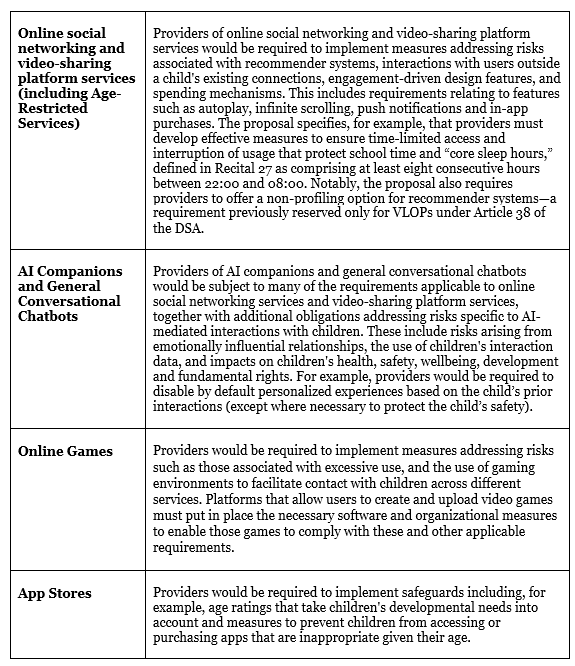
Link to What about Operating Systems? What about Operating Systems?

Unlike other Covered Services, operating systems would not be subject to the general safety-by-design obligations described above. Instead, where a provider of an operating system has obtained an age signal through age assurance that complies with the KIDS Act proposal’s requirements, it would be required, with the user’s consent, to enable the sharing of that age signal with providers of Covered Services where necessary for compliance with the KIDS Act proposal.

Link to What Other Rights, Governance and Compliance Obligations Would the KIDS Act Proposal Introduce? What Other Rights, Governance and Compliance Obligations Would the KIDS Act Proposal Introduce?

The proposal would also introduce a number of measures aimed at strengthening children’s control (so-called “agency”) over their online experience. These measures would vary depending on the type of service concerned.

  • Greater transparency and control for children. Providers of online social networking services, video-sharing platform services, online games, AI companions and general conversational chatbots would be required to present information, warnings, settings and user controls in a child-friendly and accessible manner. These providers would also be required to offer tools enabling children to influence the content and recommendations they receive, manage their settings, and easily revert to safer default configurations.
  • Codes of conduct. The Commission would facilitate the development of voluntary, EU-level codes of conduct. Codes specifically addressing age-rating and online games (Article 17) should be drawn up within one year of the date of application (i.e., approximately 18 months after entry into force). The proposal identifies the Pan-European Game Information (“PEGI”) age-classification system and code of conduct as potential examples, subject to a finding that they provide an adequate level of protection for children. As part of the release of the KIDS Act, the Commission also announced plans to develop a child-safety code of conduct for AI, focused specifically on designing algorithms suitable for children.
  • Additional governance obligations for VLOPs. One of the most significant changes in the KIDS Act is the shift in the compliance burden—rather than relying on regulators to identify and prove that a service is unsafe or non-compliant, the proposal requires certain providers to demonstrate proactively how they comply with the child-safety requirements. For DSA-designated VLOPs that are online social networking services or video-sharing platform services, this means being required to submit compliance plans to the Commission and engage independent experts to audit those plans, with corrective action plans required within 30 days where deficiencies are identified (a process that the Commission itself has referred to as a reversal of the burden of proof). The proposal would also introduce a supervisory fee for in-scope VLOPs as well as certain providers of AI companions, general conversational chatbots, and video gaming platforms, capped at 0.03% of worldwide annual net income.

Link to Enforcement Enforcement

The KIDS Act proposal would largely rely on the existing enforcement frameworks under the DSA and AI Act, with the applicable framework depending on the service or system concerned.
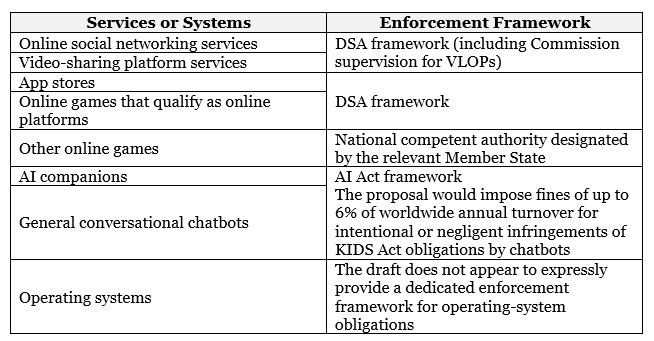
Collective complaints

Children and their guardians would be able to flag suspected violations of the KIDS Act by most providers, including through complaints submitted to national authorities and, for AI companions and general conversational chatbots, the European AI Office. They could also appoint qualified representative bodies to exercise their rights on their behalf, as the proposal would bring the KIDS Act within the scope of the Representative Actions Directive (Directive (EU) 2020/1828).

Link to Looking ahead Looking ahead

The proposal is a high political priority for the Commission and is likely to attract significant attention as it is negotiated in both the European Parliament and the Council. Given the political momentum around the protection of children online, we can expect efforts to move the negotiations forward relatively quickly.

If adopted, the Act would require covered providers to change account architecture, implement age-assurance processes, adjust recommender systems, add parental-control tools and develop product-development governance procedures (among other things). We will continue to monitor the KIDS Act and report on its progress.

Tags: AI
Photo of Dan Cooper Dan Cooper

Daniel Cooper is co-chair of Covington’s Data Privacy and Cyber Security Practice, and advises clients on information technology regulatory and policy issues, particularly data protection, consumer protection, AI, and data security matters. He has over 20 years of experience in the field, representing…

Daniel Cooper is co-chair of Covington’s Data Privacy and Cyber Security Practice, and advises clients on information technology regulatory and policy issues, particularly data protection, consumer protection, AI, and data security matters. He has over 20 years of experience in the field, representing clients in regulatory proceedings before privacy authorities in Europe and counseling them on their global compliance and government affairs strategies. Dan regularly lectures on the topic, and was instrumental in drafting the privacy standards applied in professional sport.

According to Chambers UK, his “level of expertise is second to none, but it’s also equally paired with a keen understanding of our business and direction.” It was noted that “he is very good at calibrating and helping to gauge risk.”

Dan is qualified to practice law in the United States, the United Kingdom, Ireland and Belgium. He has also been appointed to the advisory and expert boards of privacy NGOs and agencies, such as the IAPP’s European Advisory Board, Privacy International and the European security agency, ENISA.

Read more about Dan CooperEmail
Show more Show less
Photo of Dita Charanzová Dita Charanzová

Dita Charanzová advises on European policymaking and international regulatory strategy, drawing on more than two decades of experience in EU institutions and diplomacy. She served as a Member of the European Parliament from July 2014 to July 2024 and as Vice President from…

Dita Charanzová advises on European policymaking and international regulatory strategy, drawing on more than two decades of experience in EU institutions and diplomacy. She served as a Member of the European Parliament from July 2014 to July 2024 and as Vice President from July 2019 to July 2024, with responsibilities including cybersecurity and institutional relations, including relations with national parliaments, and parliamentary relations with North and South America. Her work has focused on the digital agenda, consumer protection, the internal market, and international trade.

In her advisory work, Dita, a non-lawyer, helps organizations anticipate and navigate EU policy and legislative developments—particularly at the intersection of digital regulation, internal market rules, consumer protection, and trade. She brings senior‑level insight into how priorities are shaped within the EU institutions and in particular in the European Parliament. Her experience includes high‑visibility leadership roles in the European Parliament and work on major EU digital and internal market files, including the Digital Services Act, the European Electronic Communications Code, the General Product Safety Regulation, and the Web Accessibility Directive. Dita served as a Vice-president of the Alliance of Liberals and Democrats for Europe Party from 2018 to 2023. She also previously served in the Czech diplomatic service, including a posting to the Permanent Representation to the EU, and chaired the Trade Policy Committee of the Council of the European Union during the Czech EU presidency in 2009.

Read more about Dita CharanzováEmail
Show more Show less
Photo of Jadzia Pierce Jadzia Pierce

Jadzia Pierce advises clients developing and deploying technology on a range of regulatory matters, including the intersection of AI governance and data protection. Jadzia draws on her experience in senior in house leadership roles and extensive, hands on engagement with regulators worldwide. Prior…

Jadzia Pierce advises clients developing and deploying technology on a range of regulatory matters, including the intersection of AI governance and data protection. Jadzia draws on her experience in senior in house leadership roles and extensive, hands on engagement with regulators worldwide. Prior to rejoining Covington in 2026, Jadzia served as Global Data Protection Officer at Microsoft, where she oversaw and advised on the company’s GDPR/UK GDPR program and acted as a primary point of contact for supervisory authorities on matters including AI, children’s data, advertising, and data subject rights.

Jadzia previously was Director of Microsoft’s Global Privacy Policy function and served as Associate General Counsel for Cybersecurity at McKinsey & Company. She began her career at Covington, advising Fortune 100 companies on privacy, cybersecurity, incident preparedness and response, investigations, and data driven transactions.

At Covington, Jadzia helps clients operationalize defensible, scalable approaches to AI enabled products and services, aligning privacy and security obligations with rapidly evolving regulatory frameworks across jurisdictions—with a particular focus on anticipating enforcement trends and navigating inter regulator dynamics.

Read more about Jadzia PierceEmail
Show more Show less
Photo of Anna Sophia Oberschelp de Meneses Anna Sophia Oberschelp de Meneses

Anna Sophia Oberschelp de Meneses advises on EU data protection, cybersecurity, and consumer law. Her practice covers the full range of Europe’s digital regulatory framework, including GDPR, ePrivacy, NIS2, the Cyber Resilience Act, the AI Act, the Digital Services Act, the Data Act…

Anna Sophia Oberschelp de Meneses advises on EU data protection, cybersecurity, and consumer law. Her practice covers the full range of Europe’s digital regulatory framework, including GDPR, ePrivacy, NIS2, the Cyber Resilience Act, the AI Act, the Digital Services Act, the Data Act, the European Health Data Space, and EU consumer protection law, including product safety, product liability, and consumer rights legislation. She focuses on the operational side of compliance — helping clients design policies and processes, draft documentation, and build the internal frameworks needed to meet regulatory requirements in practice.

She also advises on contentious matters, drawing on experience managing investigations before national regulators and proceedings before national courts and the Court of Justice of the European Union. She works closely with Covington’s disputes teams on matters at the intersection of regulatory compliance and litigation.

Read more about Anna Sophia Oberschelp de MenesesEmailAnna Sophia's Linkedin Profile
Show more Show less
Photo of Shona O'Donovan Shona O'Donovan

Shóna O’Donovan is an associate in the technology regulatory group in the London office. She advises clients, particularly in the technology industry, on a range of data protection, e-privacy, intermediary liability and online content issues under EU, UK, and Irish law.

Shóna provides…

Shóna O’Donovan is an associate in the technology regulatory group in the London office. She advises clients, particularly in the technology industry, on a range of data protection, e-privacy, intermediary liability and online content issues under EU, UK, and Irish law.

Shóna provides strategic advice to companies on complying with data protection, e-privacy and online content laws, as well as defending organizations in cross-border, contentious investigations and regulatory enforcement before EU and UK regulators. In this context, she has represented clients in responding to regulatory requests relating to their compliance with the GDPR, the ePrivacy Directive, the Digital Services Act, the Audiovisual Media Services Directive and the Online Safety Act 2023. She also regularly advises clients on how these laws intersect with one another.

In her current role, Shóna gained experience on secondment to the data protection team of a global technology company. In a previous role, she spent seven months on secondment to the European data protection team of a global social media company.

Shóna co-leads Covington’s pro bono work with the Schools Consent Project, and regularly delivers workshops on sexual consent in schools across London. She also regularly provides pro bono advice to non-profits on complying with data protection laws.

Read more about Shona O'DonovanEmail
Show more Show less
Photo of Sam Jungyun Choi Sam Jungyun Choi

Recognized by Law.com International as a Rising Star (2023), Sam Jungyun Choi is an associate in the technology regulatory group in Brussels. She advises leading multinationals on European and UK data protection law and new regulations and policy relating to innovative technologies, such…

Recognized by Law.com International as a Rising Star (2023), Sam Jungyun Choi is an associate in the technology regulatory group in Brussels. She advises leading multinationals on European and UK data protection law and new regulations and policy relating to innovative technologies, such as AI, digital health, and autonomous vehicles.

Sam is an expert on the EU General Data Protection Regulation (GDPR) and the UK Data Protection Act, having advised on these laws since they started to apply. In recent years, her work has evolved to include advising companies on new data and digital laws in the EU, including the AI Act, Data Act and the Digital Services Act.

Sam’s practice includes advising on regulatory, compliance and policy issues that affect leading companies in the technology, life sciences and gaming companies on laws relating to privacy and data protection, digital services and AI. She advises clients on designing of new products and services, preparing privacy documentation, and developing data and AI governance programs. She also advises clients on matters relating to children’s privacy and policy initiatives relating to online safety.

Read more about Sam Jungyun ChoiEmailSam Jungyun's Linkedin Profile
Show more Show less
Photo of Virginie de France Virginie de France

Virginie de France is an associate in the Data Privacy and Cybersecurity Practice Group. She advises clients on the full range of EU technology, data protection, and digital regulatory matters. Virginie supports clients with data protection compliance projects, assisting with investigations led by…

Virginie de France is an associate in the Data Privacy and Cybersecurity Practice Group. She advises clients on the full range of EU technology, data protection, and digital regulatory matters. Virginie supports clients with data protection compliance projects, assisting with investigations led by national authorities, and acting in litigation. She also has substantial experience helping organizations meet European and national cybersecurity obligations.

Read more about Virginie de FranceEmail
Show more Show less
Photo of Edwin Djabatey Edwin Djabatey

Edwin Djabatey is an associate in the London office. He advises on regulatory and compliance issues within, and at the intersection of, the firm’s financial services, technology, media, trade controls and white collar practices.

Reflecting an increasing trend in regulators looking beyond industry…

Edwin Djabatey is an associate in the London office. He advises on regulatory and compliance issues within, and at the intersection of, the firm’s financial services, technology, media, trade controls and white collar practices.

Reflecting an increasing trend in regulators looking beyond industry remits, Edwin acts on multi-disciplinary and cross-sectoral regulatory compliance matters. For example, he has advised global technology companies on operational resilience requirements imposed by financial services regulators.

Edwin has assisted clients on compliance matters and internal investigations – for instance, in the white collar context, concerning issues such as bribery, corruption, anti-money laundering, and fraud, and in the financial services context, concerning culture, conduct, and whistleblowing. He provides clients in the pharmaceutical, technology and energy industries with UK and EU sanctions and export controls advice. He also has experience advising clients in the technology and media industries on regulatory matters.

Read more about Edwin DjabateyEmail
Show more Show less
  • Posted in:
    Privacy and Cybersecurity, Technology and AI
  • Blog:
    Inside Privacy
  • Organization:
    Covington & Burling LLP
  • Article: View Original Source

Call us at 1-800-913-0988 or email sales@lexblog.com.

Facebook LinkedIn Twitter RSS
The Library at LexBlog
  • About LexBlog
  • The Field We Built
  • Library at LexBlog
  • Our Beliefs
  • Our Team
  • Contact LexBlog
  • Disclaimer
  • Editorial Policy
  • Terms of Service
  • Get Started
  • Publishing Solutions
  • Compass
  • Submit a Request
  • Support Center
  • System Status
Copyright © 2026, LexBlog, Inc. All Rights Reserved.
Law blog design & platform by LexBlog LexBlog Logo